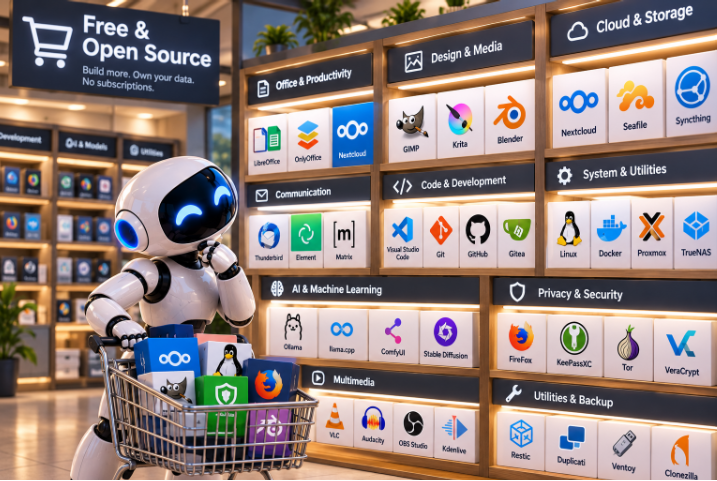
You do not have to be a programmer to benefit from GitHub. Think of it as a public workshop where people publish software projects, explain how they work, report faults and propose repairs.
Each project normally has a ‘repository’: code, documentation, a record of changes and often downloadable releases. Suppose your team needs to process hundreds of GIS files. Instead of commissioning software from scratch, you might find an open-source utility that already converts the formats. You can inspect its licence, see whether bugs are being fixed and test it on copies of non-sensitive data.
Why would someone give this away? A university may publish code so research can be reproduced. A volunteer may solve a common annoyance. A company may support a shared tool and charge for hosting, training or specialist support. This is part of the free-software economy: shared building blocks reduce the cost of making something useful.
Planetary.Blue has drawn on that economy for its own local AI experiments. Open software and modest hardware can replace some subscriptions, although setup and maintenance still cost time.
Two cautions: a public repository is not automatically open-source; check its licence. And a popular repository is not automatically safe. A malicious update or copied installation command can do damage. Test unfamiliar software in isolation before giving it access to your archive.
The benefit of GitHub is access to source code and its history. That lets a competent reviewer inspect changes and licences. Article 33 addresses a different issue: malicious skills, compromised dependencies and the permissions requested at installation.