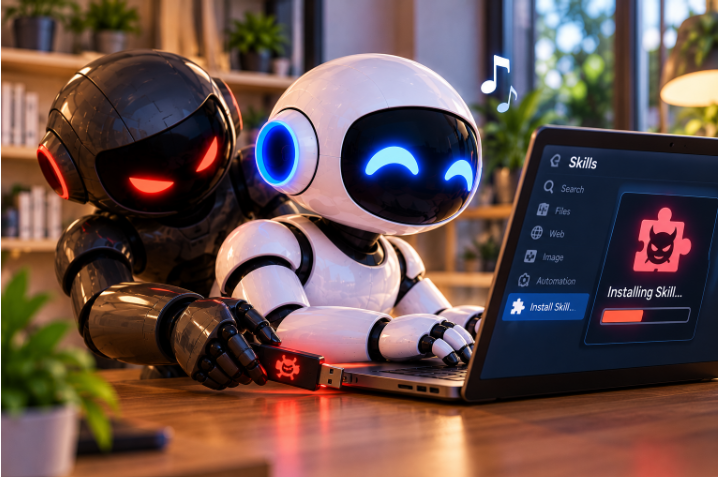
GitHub hosts enormous amounts of useful open-source software, including AI tools, model runners and agent skills. It also hosts projects that are unfinished, poorly maintained or unsafe. A public repository is not a security certificate.
An agent skill may look like a convenient way to read PDFs or search websites. But installing it can introduce third-party code, extra dependencies and permissions the user never intended. A malicious update or compromised dependency can change what the software does after the original installation.
This is why the free-software economy has two sides. Public code makes inspection and community fixes possible. It does not guarantee that somebody competent has inspected the version you downloaded. Popularity, stars and polished documentation are not substitutes for an audit.
Consider a consultancy installing a “free research assistant” from a repository. It asks for access to the whole document folder and an external API key, although its advertised function is simply to summarise public web pages. That mismatch deserves investigation before installation.
There have been published controversies involving malicious agent skills and exposed agent installations. Specific incident counts and attributions should be verified before quoting them. The practical lesson does not depend on a dramatic statistic.
Ask who maintains the software, whether releases are signed or versioned, what permissions it requires and whether independent security review exists. For members, Planetary.Blue can help assess candidate tools and vulnerabilities before they enter a working environment.